2.03 Item 1C does not say whether there are processes to oversee cybersecurity risks from third-party service providers
Company H · a US-listed aerospace services company · SEC-style question
In brief
Item 1C lists the key elements of the cybersecurity risk management program, including the use of outside firms to assess and test security. It does not say whether the company has processes to oversee and identify cybersecurity risks arising from its own use of third-party service providers, one of the three matters Regulation S-K Item 106(b)(1) asks registrants to address. Item 1A says the company makes extensive use of third-party cloud and software platforms and that some of those providers regularly experience cyberattacks, so the matter appears applicable.
The evidence, as filed
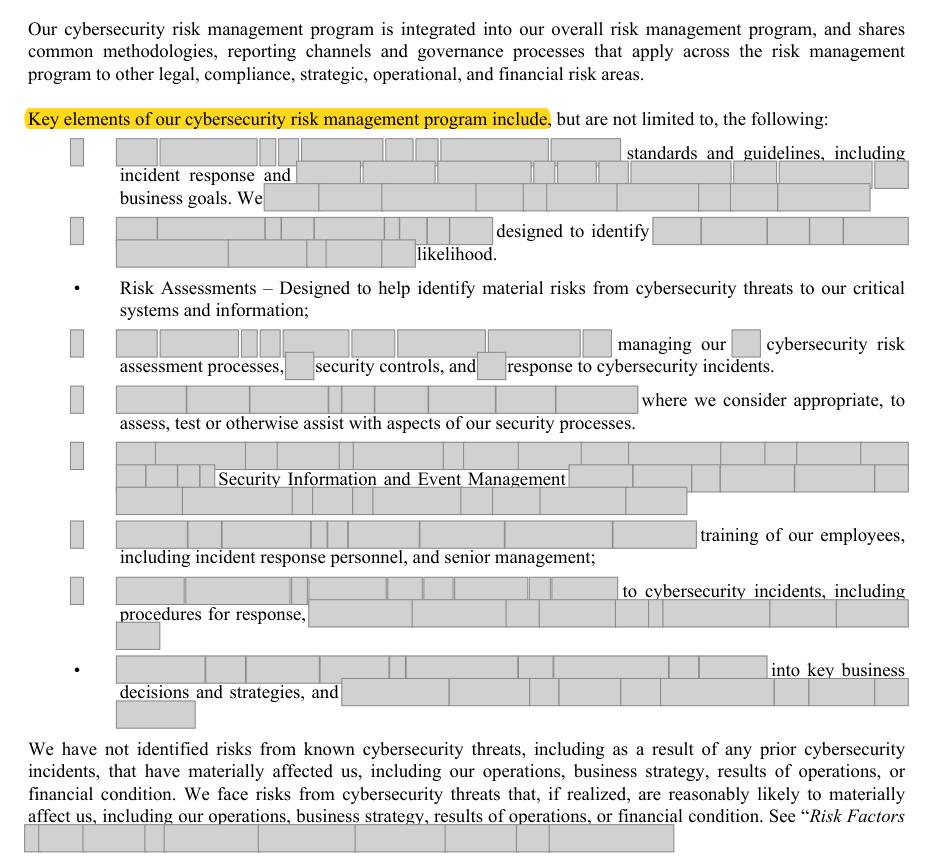
1 further page extract: screenshot withheld to protect the company’s identity. The rows below say what each shows.
What the filing shows, and what the rule requires
| What the filing shows | What the rule requires |
|---|---|
Item 1C, Risk Management and Strategy: nine bullet elements (risk governance, identification, assessments, response, 'External Service Providers - We utilize external service providers, where we consider appropriate, to assess, test or otherwise assist with aspects of our security processes', monitoring, training, incident management, integration with strategy). No statement on processes to oversee or identify cybersecurity risks from third-party service providers; the prior-year Item 1C has the same nine elements. | Either a description of the processes used to oversee and identify cybersecurity risks associated with third-party service providers (due diligence, contractual security requirements, monitoring, assessments of critical vendors), or a statement that no such processes exist. |
The rule
Regulation S-K Item 106(b)(1)(iii)
Whether the registrant has processes to oversee and identify such risks from cybersecurity threats associated with its use of any third-party service provider.
Version: Text in force at the date of this review · Source: 17 CFR 229.106 (Regulation S-K Item 106), as adopted by Release 33-11216
Regulation S-K Item 106(b)(1)
In providing such disclosure, a registrant should address, as applicable, the following non-exclusive list of disclosure items
Version: Text in force at the date of this review · Source: 17 CFR 229.106 (Regulation S-K Item 106), as adopted by Release 33-11216
Why it applies here. because the company itself describes third-party providers as a material source of cyber exposure, the third-party element is applicable; the list in Item 106(b)(1) is non-exclusive and phrased 'should address, as applicable', so whether its omission is a deficiency depends on whether such processes exist and whether management judged them immaterial to describe. That is a question for management, not a settled gap.
Why it matters
An investor cannot tell how the company manages the cyber exposure that its own risk factors attribute to third-party cloud and software providers.
How often the SEC staff raises this. In 1,100 SEC staff comment letters on fiscal 2023 and 2024 Forms 10-K, released January 2025 to October 2026, cybersecurity drew 4 of the 1,774 numbered comments (0.2%): topic 22 of 25 by frequency.
Exposure
None while the point is a question; if no answer is given, the staff may ask the company to address Item 106(b)(1)(iii) in future filings.
Our workings
Item 106(b)(1) requires a description of the processes for assessing, identifying and managing material cybersecurity risks in enough detail for a reasonable investor to understand them, and says the registrant should address, as applicable, three matters: integration with overall risk management, use of assessors and consultants, and processes to oversee and identify risks associated with its use of third-party service providers.
Item 1C addresses the first two (integration with the overall risk management program; external service providers used to assess and test security).
the third is not addressed in Item 1C or elsewhere; the whole-report search found third-party and vendor wording only in the risk factors, which describe exposure, not an oversight process.
the risk factor on p.23 says the company makes 'extensive use of [wording masked] platforms' and that it and certain of its third-party providers regularly experience cyberattacks.
| Item 106(b)(1) matter | Where addressed in Item 1C (fiscal 2025, p.47) | Status |
|---|---|---|
| (i) integration into overall risk management | 'integrated into our overall risk management program' | Addressed |
| (ii) engagement of assessors, consultants or other third parties | 'External Service Providers' bullet | Addressed |
| (iii) processes to oversee and identify risks from third-party service providers | nowhere in Item 1C or elsewhere in the report | Not addressed |
| (b)(2) material effects of cybersecurity threats | 'We have not identified risks from known cybersecurity threats ... that have materially affected us' | Addressed |
Management’s best defense, and our reply
Management would say the list in Item 106(b)(1) is expressly non-exclusive and qualified by 'as applicable', so a registrant need not address each matter, and the program description, together with the risk factors on third-party exposure, gives a reasonable investor enough to understand the processes. It may also say third-party risk is covered within the 'Risk Governance' and 'Risk Assessments' elements. However, the item frames the third matter as 'whether' such processes exist, the company's own risk factors make third-party providers a material channel of cyber risk, and neither named element refers to vendors; whether processes exist is a fact only management can confirm, which is why this is put as a question.
The fix
- Add a bullet such as: 'Third-Party Risk Management - We assess the security practices of third-party service providers with access to our systems or data before engagement and periodically thereafter, and require contractual security and incident-notification terms.'
Question for the company
Does the company have processes to oversee and identify cybersecurity risks associated with its use of third-party service providers (for example due diligence, contractual security terms and monitoring of critical cloud and software vendors), and if so, why are they not described in Item 1C?
Evidence relied on
| # | What it shows | Type | Where |
|---|---|---|---|
| 1 | the only third-party element in Item 1C concerns outside firms used to assess and test security | Document | Form 10-K 2025, page 47 |
| 2 | the integration element of Item 106(b)(1)(i) is addressed | Document | Form 10-K 2025, page 47 |
| 3 | Item 1A describes extensive reliance on third-party cloud and software providers | Document | Form 10-K 2025, page 23 |
| 4 | Item 1A says third-party providers regularly experience cyberattacks | Document | Form 10-K 2025, page 23 |
Absence check
- Document
- Form 10-K 2025
- Where it would appear
- Key elements of our cybersecurity risk management program include
- What is missing
- any statement on processes to oversee and identify cybersecurity risks associated with the use of third-party service providers
- Pages looked at
- p.46-48 (Item 1C), p.22-25 (cybersecurity risk factors)
- Result
- 'vendor' hits p.8, [n]: supplier selection and risk-factor descriptions of exposure, not an oversight process; 'oversee' hits p.47 (the Audit Committee oversees the program) and p.137-138 (officer biographies); 'service provider' hits p.6-7 and 14-16 (the company as [wording masked]), p.25 (contract terms with providers processing [state] residents' data, a privacy-law compliance step), p.27 (disruptions at service providers), p.34, p.47 (the assessors bullet) and p.115 (equity plan); 'third-party service provider' and 'supplier risk' have no hits.
Prepared by Pramanex from the company’s public SEC filings, without the company’s involvement, to show how a 10-K Pre-filing Check reads. The company is not named, and nothing on this page is a statement about any identifiable company. Observations are not an audit, review or other attestation or assurance engagement, and not legal advice. An SEC-style question is a question, not a conclusion.
Want this on your own 10-K, before you file?
Start with three free findings on your latest 10-K, or book a fixed-price 10-K Pre-filing Check.
Your next 10-K will be in draft before the audit is done.
Have it read before you file.
Start with three free findings on your latest 10-K, or book a fixed-price 10-K check. Drafts only under NDA, inside your insider trading policy.