2.01 Item 1C names the officers who manage cybersecurity risk but no longer describes their expertise
Company H · a US-listed aerospace services company · Compliance or disclosure gap
In brief
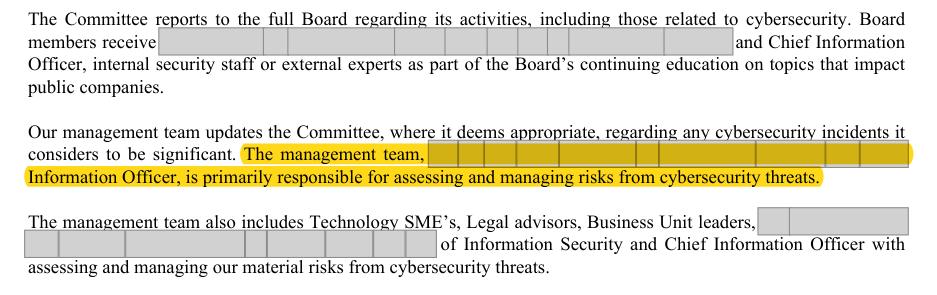
Item 1C says the management team that assesses and manages cybersecurity risk is led by the Vice President of Information Security and Chief Information Officer. Regulation S-K Item 106(c)(2)(i) asks for the relevant expertise of the persons responsible, in enough detail to describe its nature. The fiscal 2025 Form 10-K gives no such description anywhere, although the prior-year Form 10-K described the experience and degrees of both officers then responsible.
The evidence, as filed
1 further page extract: screenshot withheld to protect the company’s identity. The rows below say what each shows.
What the filing shows, and what the rule requires
| What the filing shows | What the rule requires |
|---|---|
Item 1C names the Vice President of Information Security and Chief Information Officer as leading cybersecurity risk management, then describes the supporting team and information flows; no experience, degrees, certifications or background in cybersecurity is given for either role. | For each management position named as responsible, a description of the relevant cybersecurity expertise (prior work experience in cybersecurity, relevant degrees or certifications, other knowledge or background), as the prior-year Form 10-K provided. |
The rule
Regulation S-K Item 106(c)(2)(i)
Whether and which management positions or committees are responsible for assessing and managing such risks, and the relevant expertise of such persons or members in such detail as necessary to fully describe the nature of the expertise
Version: Text in force at the date of this review · Source: 17 CFR 229.106 (Regulation S-K Item 106), as adopted by Release 33-11216
Regulation S-K Item 106, Instruction 2 to Item 106(c)
Relevant expertise of management in Item 106(c)(2)(i) may include, for example: Prior work experience in cybersecurity; any relevant degrees or certifications; any knowledge, skills, or other background in cybersecurity.
Version: Text in force at the date of this review · Source: 17 CFR 229.106 (Regulation S-K Item 106), as adopted by Release 33-11216
Form 10-K, Part I, Item 1C
Furnish the information required by Item 106 of Regulation S-K
Version: Text in force at the date of this review · Source: Form 10-K General Instructions and items, as amended by Release 33-11216
Why it applies here. Every other Item 106(c) element is present; only the expertise element is missing. The fiscal 2024 Item 1C gave a bullet for each responsible officer, for example 'He has over 20 years of information technology experience, including leadership experience managing global information security'. That report named a Senior Vice President of Information Technology; this year's titles differ.
Why it matters
- Investors cannot judge whether the persons now responsible for cybersecurity risk have relevant expertise, a point the Commission singled out when it adopted Item 106.
- A staff comment asking for the description in future filings is the realistic outcome; no fine applies.
How often the SEC staff raises this. In 1,100 SEC staff comment letters on fiscal 2023 and 2024 Forms 10-K, released January 2025 to October 2026, cybersecurity drew 4 of the 1,774 numbered comments (0.2%): topic 22 of 25 by frequency.
Exposure
No fixed penalty. The realistic consequence is a staff comment asking the company to describe the expertise and to undertake to do so in future filings; an amendment is unlikely for this element alone.
Our workings
Item 1C identifies the Audit Committee as the board committee overseeing cybersecurity, names the Vice President of Information Security and Chief Information Officer as leading the management team primarily responsible for assessing and managing cybersecurity risk, lists the supporting functions, and describes how management stays informed. It contains no statement of either officer's experience, qualifications or background. The prior-year Form 10-K (fiscal 2024) carried a bullet for each responsible officer setting out years of information technology experience, prior security roles and degrees.
the expertise terms searched across the whole fiscal 2025 report hit only the remediation of internal control and the Part III biographies of directors and executive officers, none of which covers the cybersecurity officers.
none; this is a disclosure-element test (matrix in the workings).
of the elements in Item 106(c), board oversight, the responsible committee, the processes by which management is informed and the reporting line to the Committee are present; only the expertise element of paragraph (c)(2)(i) is missing. The officer titles also changed between the two reports (the prior year named a Senior Vice President of Information Technology; this year a 'Vice President of Information Security and Chief Information Officer', which the page lists as a single item and may be one combined role), so the reader cannot tell whether the expertise previously described still sits with the persons now responsible.
| Item 106 element | Where in Item 1C (fiscal 2025) | Status |
|---|---|---|
| (c)(1) board oversight and committee | Cybersecurity Governance, first paragraph (Audit Committee) | Present |
| (c)(1) how the board or committee is informed | Committee reports to the full Board; presentations to Board members | Present |
| (c)(2)(i) positions responsible | management team led by the [wording masked] | Present |
| (c)(2)(i) relevant expertise of those persons | nowhere in Item 1C or elsewhere in the report | Absent |
| (c)(2)(ii) how persons are informed and monitor incidents | briefings, threat intelligence, security tool alerts | Present |
| (c)(2)(iii) reporting to the board or committee | management updates the Committee on significant incidents | Present |
Management’s best defense, and our reply
Management may argue that Item 106(c)(2) lists its sub-items as a non-exclusive list to be addressed 'as applicable', that the core requirement is to describe management's role, and that the report does so by naming the positions, the supporting team and the information flows. It may add that the officers responsible changed during the year and that the expertise detail is not material to an investor's decision. However, paragraph (c)(2)(i) applies whenever positions are named, as here, and the Commission's instruction spells out the kind of detail expected; nothing in the report incorporates the description from another document, and the company's own prior-year Form 10-K gave it, so the omission reads as a drafting loss rather than a considered materiality judgment.
The fix
- In the next Form 10-K add, after the sentence naming the responsible officers, one bullet per officer, e.g. 'Our Vice President of Information Security has [n] years of experience in information security, including [prior roles], and holds [degrees / certifications]'; do the same for the Chief Information Officer if that role is held by a separate person.
Evidence relied on
| # | What it shows | Type | Where |
|---|---|---|---|
| 1 | names the management positions responsible for cybersecurity risk, with no description of their expertise | Document | Form 10-K 2025, page 48 |
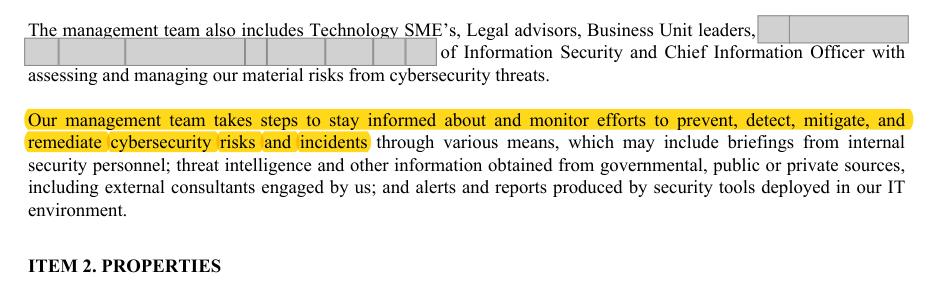
| 2 | the closing paragraph of Item 1C governance covers how management is informed; Item 2 follows directly, with no expertise description in between | Document | Form 10-K 2025, page 48 |
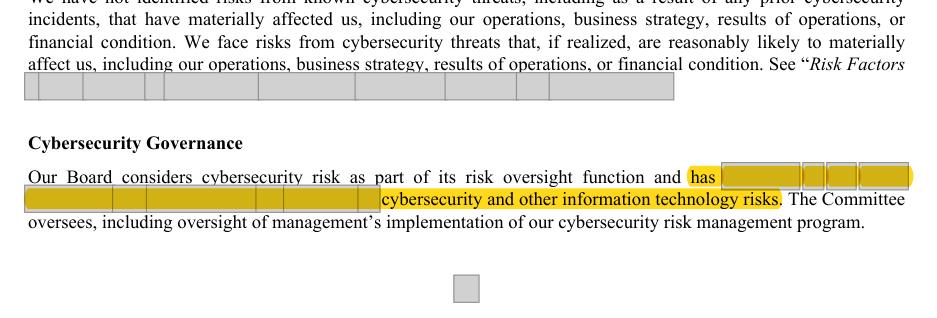
| 3 | board oversight and the responsible committee are disclosed, so the gap is confined to management expertise | Document | Form 10-K 2025, page 47 |
Absence check
- Document
- Form 10-K 2025
- Where it would appear
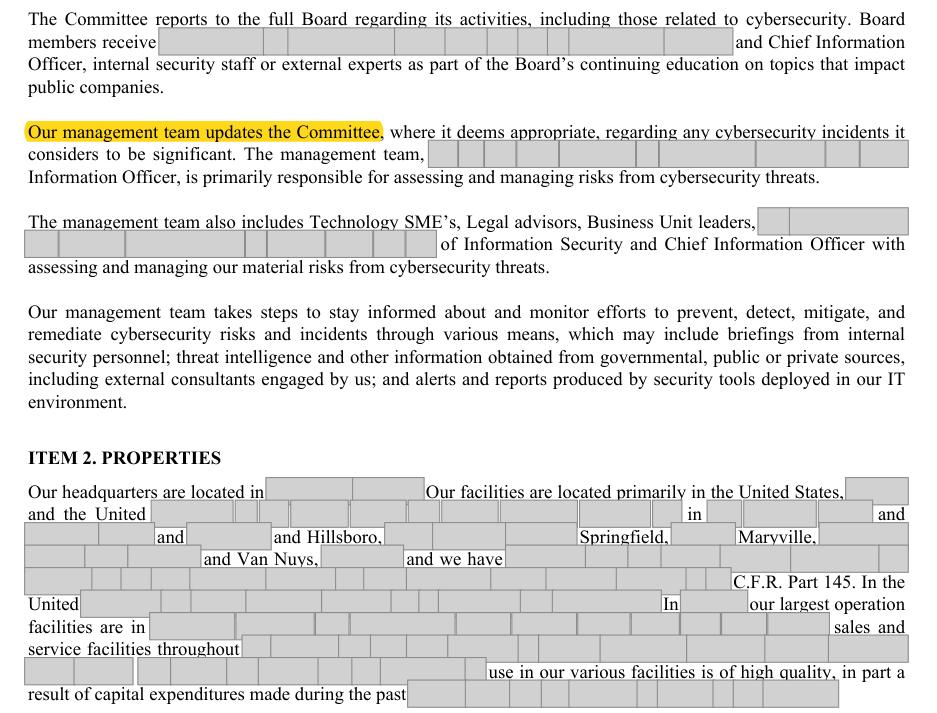
- Our management team updates the Committee
- What is missing
- a description of the relevant cybersecurity expertise of the Vice President of Information Security and of the Chief Information Officer named as responsible
- Pages looked at
- p.46-48 (Item 1C in full)
- Result
- 'expertise' hits p.131-133 (advisers and IT personnel hired for internal-control remediation) and p.135-138 (Part III biographies of directors and executive officers); 'years of experience' and 'holds a Bachelor' hit only those Part III biographies, none of which is a cybersecurity officer; 'Information Security' hits only p.48, the sentences naming the role; 'CISO' and 'information technology experience' have no hits.
Prepared by Pramanex from the company’s public SEC filings, without the company’s involvement, to show how a 10-K Pre-filing Check reads. The company is not named, and nothing on this page is a statement about any identifiable company. Observations are not an audit, review or other attestation or assurance engagement, and not legal advice. An SEC-style question is a question, not a conclusion.
Want this on your own 10-K, before you file?
Start with three free findings on your latest 10-K, or book a fixed-price 10-K Pre-filing Check.
Your next 10-K will be in draft before the audit is done.
Have it read before you file.
Start with three free findings on your latest 10-K, or book a fixed-price 10-K check. Drafts only under NDA, inside your insider trading policy.