2.03 Item 1C names the executives who lead cybersecurity but describes their expertise only in general terms
Company E · a US-listed home furnishings retailer · SEC-style question
In brief
Item 1C says cybersecurity risk management is led by the Chief Information Officer (CIO), the Chief Information Security Officer (CISO) and a dedicated team 'with experience across multiple industries in various roles involving managing information security'. Item 106(c)(2)(i) asks for the relevant expertise of the persons responsible in enough detail to describe its nature. The CIO's technology career is set out among the executive officers in Item 10, but nothing in the 10-K describes the CISO's expertise. We ask whether the company regards the description as complete, since the 2024 Form 10-K was similar.
The evidence, as filed
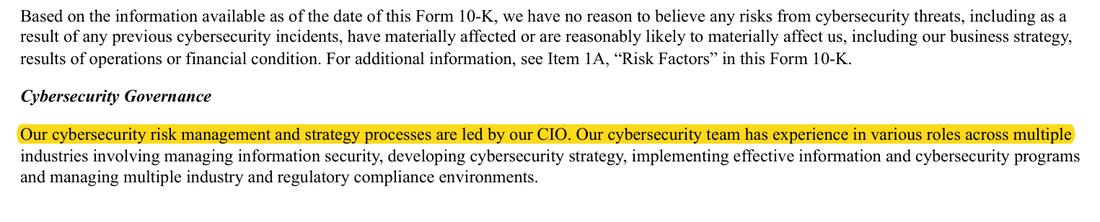
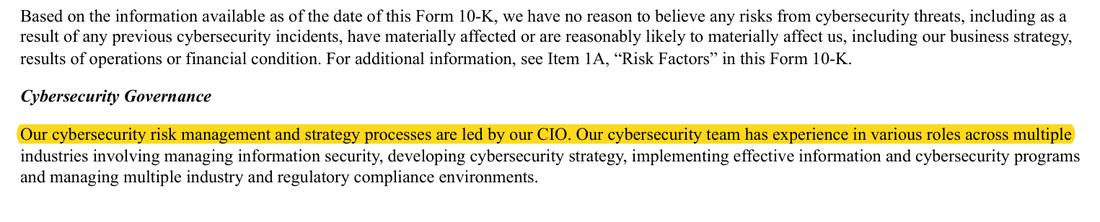
2 further page extracts: screenshot withheld to protect the company’s identity. The rows below say what each shows.
What the filing shows, and what the rule requires
| What the filing shows | What the rule requires |
|---|---|
Cybersecurity Governance names the CIO and CISO and describes experience in one sentence covering the leaders and the team together; the CIO's profile in Item 10 lists technology and application-development roles; no expertise of the CISO is described anywhere. | A short statement of the nature of the CISO's relevant expertise (for example prior information-security roles or certifications), and a pointer from Item 1C to the CIO's profile, or confirmation that the company regards the present description as complete. |
| What we checked. Item 1C in full against each Item 106 element; Item 10 executive officer biographies for any CIO or CISO profile; the 2024 Form 10-K Item 1C; the Form 8-K list for any Item 1.05 cybersecurity incident report (none). | |
The rule
Regulation S-K Item 106(c)(2)(i), management's role
Whether and which management positions or committees are responsible for assessing and managing such risks, and the relevant expertise of such persons or members in such detail as necessary to fully describe the nature of the expertise;
Version: Text in force at the date of this review · Source: Regulation S-K, 17 CFR 229.106(c)(2)(i), as adopted by Release 33-11216 (2023)
Regulation S-K Item 106(c), Instruction 2
Relevant expertise of management in Item 106(c)(2)(i) may include, for example: Prior work experience in cybersecurity; any relevant degrees or certifications; any knowledge, skills, or other background in cybersecurity.
Version: Text in force at the date of this review · Source: Regulation S-K, 17 CFR 229.106, Instructions to Item 106(c), as adopted by Release 33-11216 (2023)
Why it applies here. Item 106(c)(2)(i) requires the relevant expertise of the persons responsible 'in such detail as necessary to fully describe the nature of the expertise', and Instruction 2 lists prior work experience, degrees and certifications as examples. The experience sentence can be read as covering the leaders and the team together, the CIO's career is given elsewhere in the same 10-K, and the rule does not require names, biographies or any one of the listed examples; on that reading the element is given in general terms. Whether that describes the nature of the CISO's expertise is a judgment for the company, so the point is put as a question. Every other Item 106 element tested was given.
Why it matters
If the description is read as covering only the team, investors cannot judge the expertise of the CISO, who implements the cybersecurity program, which is the purpose of the Item 106(c)(2)(i) disclosure.
Exposure
None while this remains a question; if the description is held insufficient, the usual course is a staff comment and a fuller description in future filings.
Our workings
Item 1C describes a NIST-based program, outside advisers, third-party risk processes, the Technology Committee's oversight and a statement that no cybersecurity threat has materially affected the company. On management, it says the program is led by the CIO, the CISO 'and a dedicated cybersecurity team with experience across multiple industries in various roles involving managing information security', developing strategy, implementing programs and managing compliance environments. The CIO is profiled among the executive officers in Item 10: chief technology officer at another retailer and earlier eCommerce-technology, application-development and logistics-engineering roles; Item 1C does not refer to that profile. The CISO is not described anywhere. The 2024 Form 10-K said the program was led by the CIO and that the team had experience in various roles across multiple industries.
| Item 106 element | Where given | Status |
|---|---|---|
| (b)(1) processes, integration with risk management | p.37 | Given |
| (b)(1)(ii) assessors and consultants engaged | p.37 | Given |
| (b)(1)(iii) third-party service provider risk | p.38 | Given |
| (b)(2) material effects of threats | p.38 | Given |
| (c)(1) board committee oversight and how informed | p.38 | Given |
| (c)(2)(i) positions responsible and their expertise | p.38 | Given in general terms: positions named, one shared experience sentence |
| (c)(2)(ii)-(iii) how informed; reporting to the board | p.38 | Given |
Management’s best defense, and our reply
The company would say that the experience sentence describes the CIO, the CISO and the team together and states the nature of that experience: managing information security, developing cybersecurity strategy, implementing programs and managing regulatory compliance across industries. It would add that the CIO's technology career is set out in Item 10 of the same 10-K, that Item 106 is principles-based, that Instruction 2 gives examples rather than requirements, and that the Commission declined to require named individuals or biographies. That reading is tenable, which is why the point is a question rather than a finding. The answer is that the rule speaks of the expertise of the persons responsible in enough detail to describe its nature; nothing shows what the CISO brings, and a line on the CISO with a pointer to the CIO's profile removes the doubt at no cost.
The fix
- Add, e.g.: 'Our CISO has [x] years of information-security experience, including [prior roles], and holds [certification]; our CIO has [x] years of technology leadership experience including oversight of cybersecurity programs.'
Question for the company
Does the company regard the shared sentence on the experience of the CIO, the CISO and the cybersecurity team, together with the CIO's profile in Item 10, as describing the nature of the expertise of the persons responsible for cybersecurity risk, as Item 106(c)(2)(i) asks, or will the next Form 10-K describe the CISO's relevant experience?
Evidence relied on
| # | What it shows | Type | Where |
|---|---|---|---|
| 1 | the responsible positions are named | Document | Form 10-K 2025, page 38 |
| 2 | the only description of expertise in Item 1C is one sentence covering the leaders and the team together | Document | Form 10-K 2025, page 38 |
| 3 | the 2024 Form 10-K gave the same generic description | Document | Form 10-K 2024 (prior year), page 42 |
| 4 | the CIO's profile in Item 10 gives technology roles, not cybersecurity expertise; there is no CISO profile | Document | Form 10-K 2025, page 87 |
Absence check
- Document
- Form 10-K 2025
- Where it would appear
- Cybersecurity Governance
- What is missing
- the relevant expertise (prior roles, degrees or certifications) of the CISO, and any reference from Item 1C to the CIO profile in Item 10
- Pages looked at
- p.37-38 (Item 1C) and p.87-88 (Item 10 executive officers)
- Result
- 'years of experience' does not appear anywhere; 'degree' hits only the phrase 'high degree' (p.4, 5, [n] and the auditor's report on p.54), never an academic degree; 'certification' hits payment-card certification requirements and the officer certifications listed among the exhibits, not cybersecurity credentials; 'expertise' hits p.6 (design consultants), p.18 and [n] (internal-control remediation taskforce), none describing the CIO or CISO.
Prepared by Pramanex from the company’s public SEC filings, without the company’s involvement, to show how a 10-K Pre-filing Check reads. The company is not named, and nothing on this page is a statement about any identifiable company. Observations are not an audit, review or other attestation or assurance engagement, and not legal advice. An SEC-style question is a question, not a conclusion.
Want this on your own 10-K, before you file?
Start with three free findings on your latest 10-K, or book a fixed-price 10-K Pre-filing Check.
Your next 10-K will be in draft before the audit is done.
Have it read before you file.
Start with three free findings on your latest 10-K, or book a fixed-price 10-K check. Drafts only under NDA, inside your insider trading policy.