2.01 Item 1C does not say whether cybersecurity risks have materially affected the company
Company G · a US-listed specialty pharmaceutical company · Compliance or disclosure gap
In brief
Regulation S-K Item 106(b)(2) asks the company to describe whether cybersecurity risks, including those from previous incidents, have materially affected or are reasonably likely to materially affect it. Item 1C answers only by pointing to a risk factor about risks that 'may materially affect us'. That risk factor is written wholly in the conditional ('If we ... experience a security incident') and never says whether any risk or past incident has had a material effect. The same wording was used in the prior-year Form 10-K.
The evidence, as filed
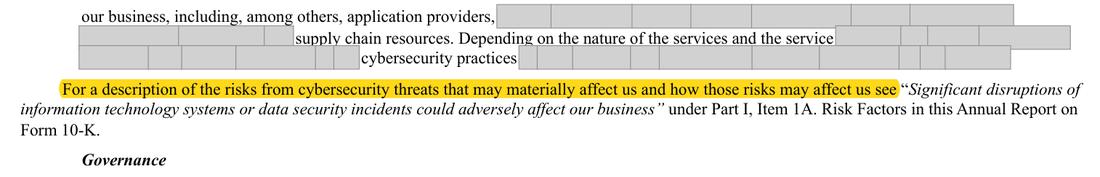
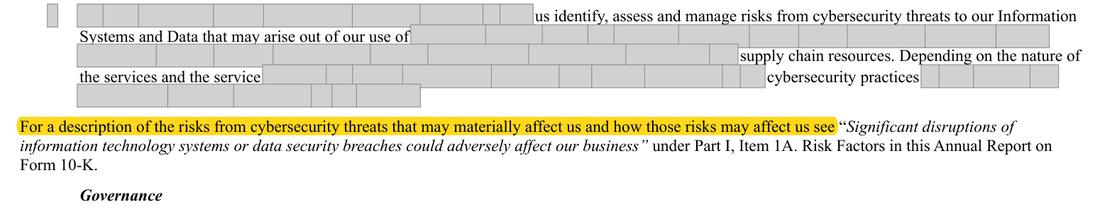
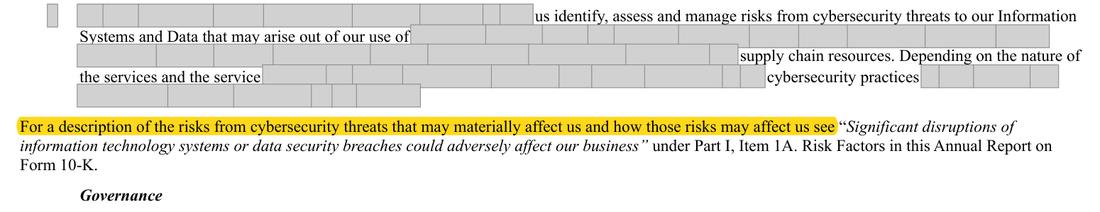
1 further page extract: screenshot withheld to protect the company’s identity. The rows below say what each shows.
What the filing shows, and what the rule requires
| What the filing shows | What the rule requires |
|---|---|
Item 1C cross-refers to the risk factor 'Significant disruptions of information technology systems or data security incidents could adversely affect our business'; neither Item 1C nor the risk factor states whether cybersecurity risks or previous incidents have materially affected the company. | A direct statement, for example: 'We have not identified any risks from cybersecurity threats, including as a result of any previous cybersecurity incidents, that have materially affected us, including our business strategy, results of operations or financial condition', followed by the cross-reference for the forward-looking part. |
| What we checked. Item 1C element by element against Item 106(b)(1) to (c)(2); the cross-referred risk factor; whole-document search; prior-year Item 1C; Form 8-K Item 1.05 and [n] filings for the period. | |
The rule
Regulation S-K Item 106(b)(2)
Describe whether any risks from cybersecurity threats, including as a result of any previous cybersecurity incidents, have materially affected or are reasonably likely to materially affect the registrant, including its business strategy, results of operations, or financial condition and if so, how.
Version: Text in force at the date of this review · Source: Regulation S-K Item 106 (17 CFR 229.106), as adopted by Release 33-11216
Why it applies here. The cross-reference covers at most the forward-looking part ('reasonably likely to'); the backward-looking part ('have materially affected') is not answered. No Form 8-K Item 1.05 (material cybersecurity incident) was filed for the period, so the answer is probably no, but the 10-K must say so.
Why it matters
- An investor cannot tell from the filing whether past cybersecurity incidents have had any material effect.
- A staff comment asking for the statement in future filings is the realistic outcome; no fine attaches, and one sentence cures the gap.
How often the SEC staff raises this. In 1,100 SEC staff comment letters on fiscal 2023 and 2024 Forms 10-K, released January 2025 to October 2026, cybersecurity drew 4 of the 1,774 numbered comments (0.2%): topic 22 of 25 by frequency.
Exposure
A staff comment asking for the statement in future filings; no fine attaches to this disclosure gap.
Our workings
Item 1C describes processes (Item 106(b)(1)(i)-(iii)), board oversight through the Audit Committee ((c)(1)) and management roles with the expertise of the Chief Information Security Officer (CISO) and Chief Digital Officer (CDO) ((c)(2)). For (b)(2) it says only: 'For a description of the risks from cybersecurity threats that may materially affect us and how those risks may affect us see' the risk factor. That risk factor, on printed pages 61-62, is conditional throughout ('If we (or a third party upon whom we rely) experience a security incident ...'). No sentence in the document says whether any risk or previous incident has materially affected the company.
Item 106(b)(2) has two limbs - a backward-looking one ('have materially affected') and a forward-looking one ('are reasonably likely to materially affect'). The cross-reference covers, at most, the forward limb; the backward limb is not answered. The rule's wording ('describe whether ... and if so, how') calls for a statement either way, which is why many filers include a negative statement. No Form 8-K Item 1.05 was filed for the period, so the answer is probably negative, but the Form 10-K must say so.
| Item 106 element | Where in Item 1C | Status |
|---|---|---|
| (b)(1)(i) integration with overall risk management | Printed page 75, third bullet (risk register, enterprise risk management) | Present |
| (b)(1)(ii) assessors, consultants, third parties | Printed page 75, fourth bullet | Present |
| (b)(1)(iii) third-party service-provider risk | Printed pages 75-76, fifth bullet | Present |
| (b)(2) whether risks have materially affected | Printed page 76 cross-reference only; risk factor on printed pages 61-62 is conditional | Not stated |
| (b)(2) whether risks are reasonably likely to materially affect | Printed page 76 cross-reference to the risk factor | Covered by cross-reference |
| (c)(1) board oversight and committee | Printed page 76, Governance bullets 1-2 | Present |
| (c)(2) management roles, expertise, reporting | Printed page 76, Governance bullets 3-4 | Present |
Management’s best defense, and our reply
Management would say the cross-reference to a detailed risk factor is a permitted way of answering Item 106(b)(2), and that the absence of any Form 8-K Item 1.05 filing tells investors that no incident has been material. They would add that the staff reviewed the prior-year Form 10-K in July and [date] and did not comment on Item 1C. However, the cross-reference addresses only risks that 'may' affect the company; the rule also asks whether risks 'have materially affected' it, and silence is not a description. A staff review that raised no comment is not approval, and the gap is cured by one sentence.
The fix
- Add to Item 1C: 'As of the date of this report, we have not identified any risks from cybersecurity threats, including as a result of any previous cybersecurity incidents, that have materially affected us, including our business strategy, results of operations or financial condition', keeping the risk-factor cross-reference for the forward-looking part.
Evidence relied on
| # | What it shows | Type | Where |
|---|---|---|---|
| 1 | Item 1C's only response to the material-effect element is a cross-reference about risks that may affect the company | Document | Form 10-K 2025, page 76 |
| 2 | The cross-referred risk factor is conditional and does not say whether any risk or incident has had a material effect | Document | Form 10-K 2025, page 62 |
| 3 | Item 1C risk management and strategy section, where the material-effect statement belongs | Document | Form 10-K 2025, page 75 |
| 4 | The fiscal 2024 Item 1C deals with the effect of cybersecurity risks only by this cross-reference to a risk factor | Document | Form 10-K 2024 (prior year), page 72 |
| 5 | The risk factor referred to is headed as what could happen | Document | Form 10-K 2024 (prior year), page 58 |
| 6 | The risk factor is written in the conditional and says nothing about any past or reasonably likely material effect | Document | Form 10-K 2024 (prior year), page 58 |
| 7 | The risk factor that Item 1C cross-refers to is captioned in the conditional ('could adversely affect') | Document | Form 10-K 2025, page 61 |
| 8 | The risk factor closes on what security measures may fail to prevent, again in the future tense | Document | Form 10-K 2025, page 62 |
Absence check
- Document
- Form 10-K 2025
- Where it would appear
- For a description of the risks from cybersecurity threats
- What is missing
- a statement whether risks from cybersecurity threats, including previous incidents, have materially affected the company
- Pages looked at
- p.61-62 (cybersecurity risk factor), p.75-76 (Item 1C)
- Result
- 'materially affected' hits p.70 (debt refinancing risk) and p.107 (changes in internal control); 'reasonably likely to materially affect' hits p.107 only (internal control); 'cybersecurity incident' hits p.51 (Russia sanctions risk), p.75 (third parties assist in an incident) and p.76 (incident response plan escalation and reporting to the Audit Committee, including incidents 'that have potentially had a material impact') - none states whether cybersecurity risks or incidents have materially affected the company. 'have not identified', 'not materially affected' and 'previous cybersecurity incident' do not hit.
Absence check
- Document
- Form 10-K 2024 (prior year)
- Where it would appear
- For a description of the risks from cybersecurity threats
- What is missing
- a statement whether cybersecurity risks, including those from previous incidents, have materially affected or are reasonably likely to materially affect the company
- Pages looked at
- Form 10-K 2024 (prior year) p.58-59 (risk factor), p.71-72 (Item 1C)
- Result
- 'materially affected' hits p.66 (debt refinancing risk factor) and p.102 (changes in internal control); 'reasonably likely to materially affect' hits only p.102 (changes in internal control); 'have not experienced' hits only financial-statement pages (printed F-n; see folios) (credit losses on receivables); 'previous incidents' and 'material cybersecurity' do not hit: none of the hits is a statement about cybersecurity risks
Prepared by Pramanex from the company’s public SEC filings, without the company’s involvement, to show how a 10-K Pre-filing Check reads. The company is not named, and nothing on this page is a statement about any identifiable company. Observations are not an audit, review or other attestation or assurance engagement, and not legal advice. An SEC-style question is a question, not a conclusion.
Want this on your own 10-K, before you file?
Start with three free findings on your latest 10-K, or book a fixed-price 10-K Pre-filing Check.
Your next 10-K will be in draft before the audit is done.
Have it read before you file.
Start with three free findings on your latest 10-K, or book a fixed-price 10-K check. Drafts only under NDA, inside your insider trading policy.